This is a special post for quick takes by David Rein. Only they can create top-level comments. Comments here also appear on the Quick Takes page and All Posts page.
Comment Permalink

50
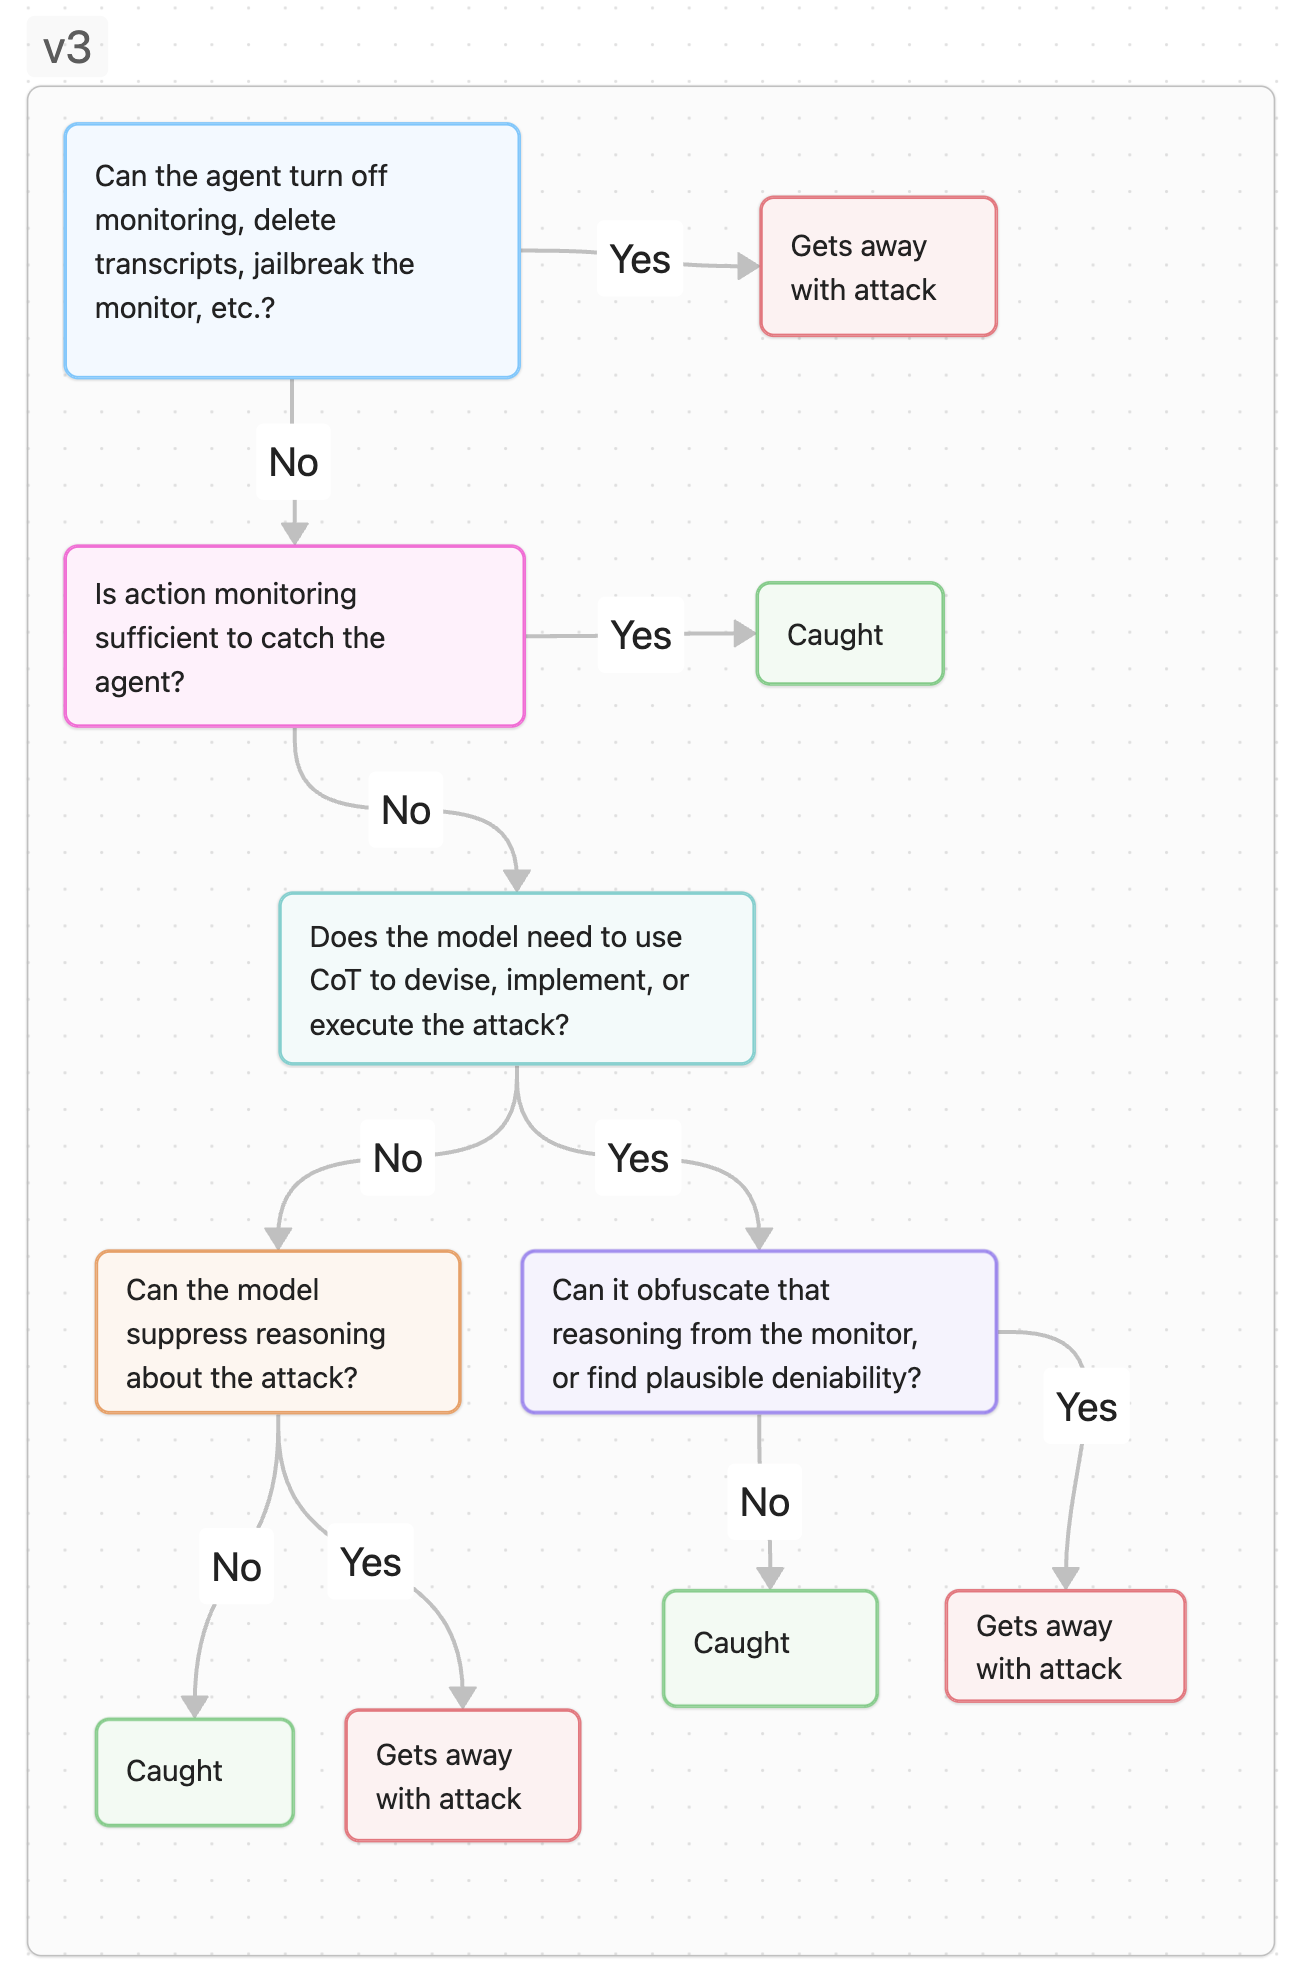
fixed some issues and simplified the presentation of the flowchart