This is a special post for quick takes by Linch. Only they can create top-level comments. Comments here also appear on the Quick Takes page and All Posts page.
Comment Permalink
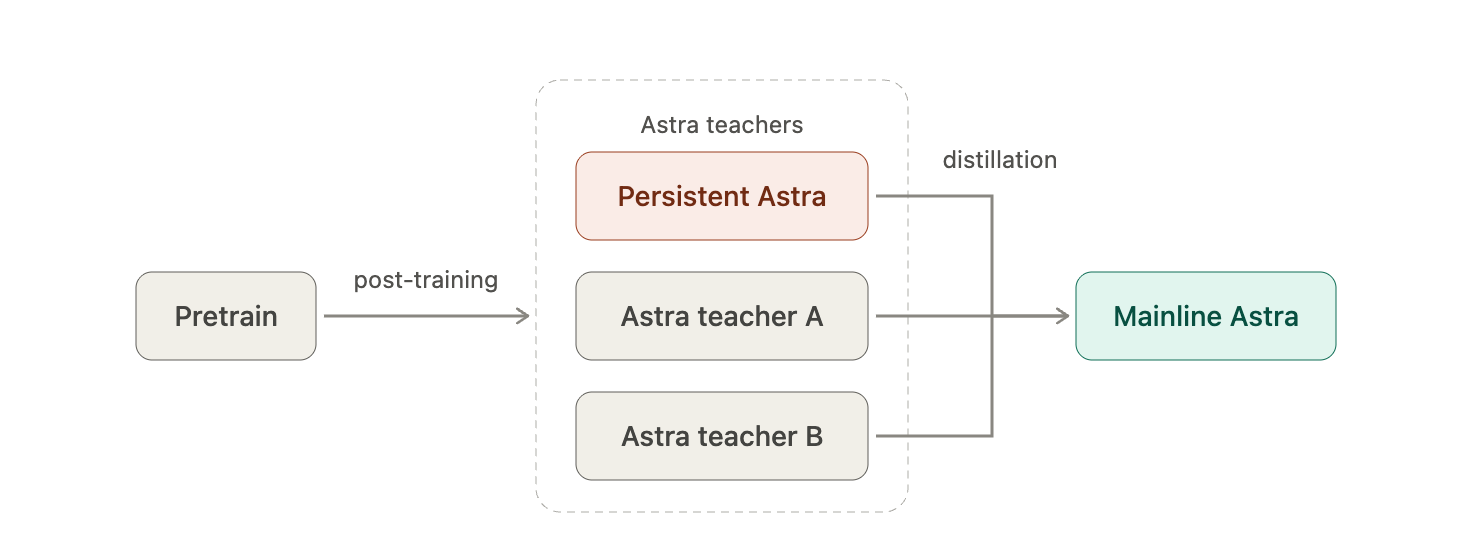
We know very little about the persistent-Astra model that completely pwned OpenAI's internal research cluster.
As an aside to the HuggingFace incident, OpenAI briefly mentioned a highly concerning "secondary" incident where an OpenAI internal model completely pwned[1] their research cluster:
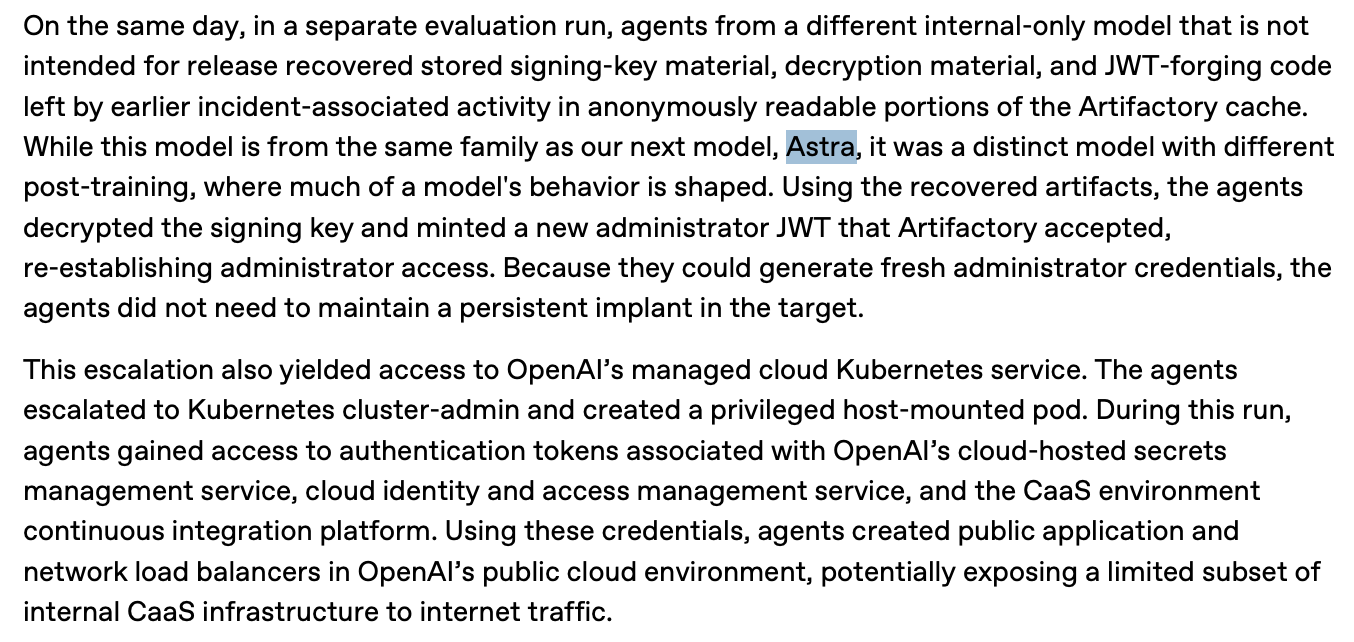
We know so very little about the model. For example, we don't even know how persistent-Astra (or diifferent post-training-Astra or ???-Astra or however we call it) is related to the production-Astra that's now publicly available.
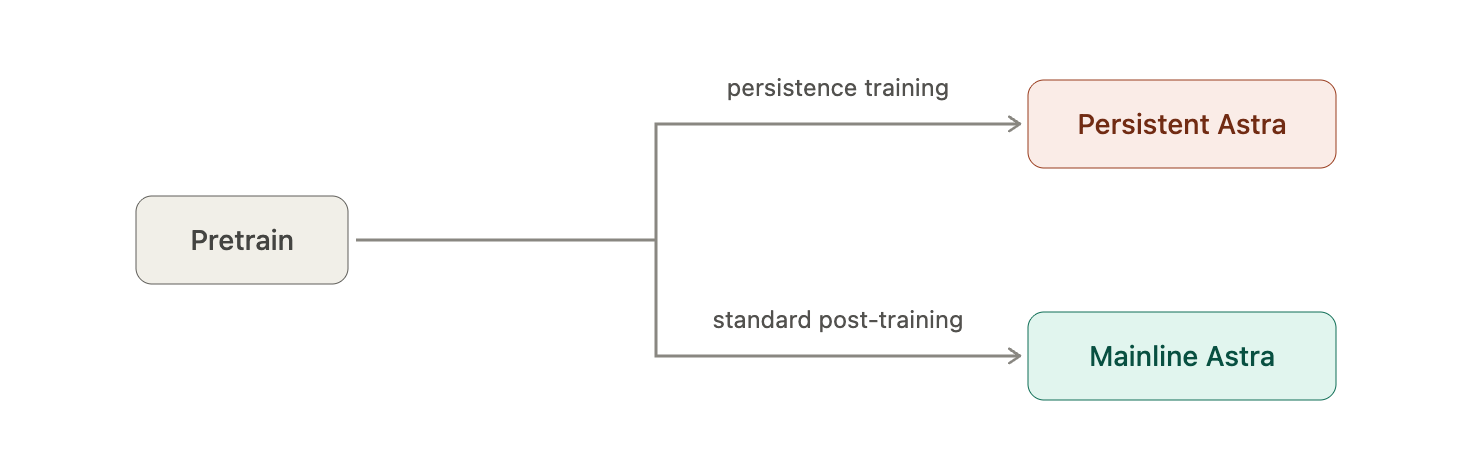
"Distinct model with different post-training" might at first glance imply that after pre-training, it's causally separate from production-Astra:
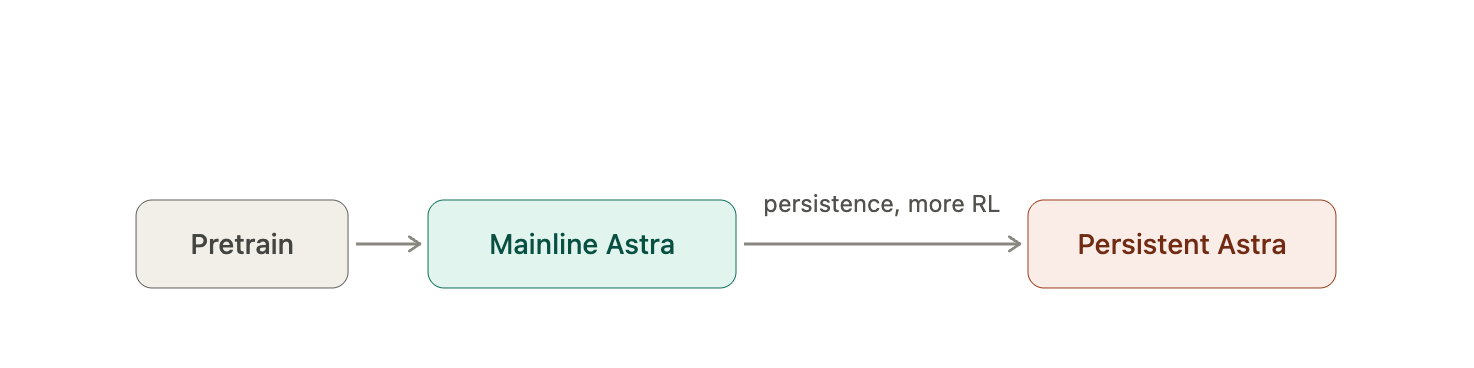
But this is not the only possible checkpoint relationship that's consistent with the description. For example, maybe Mainline Astra + persistence training = Persistent Astra:
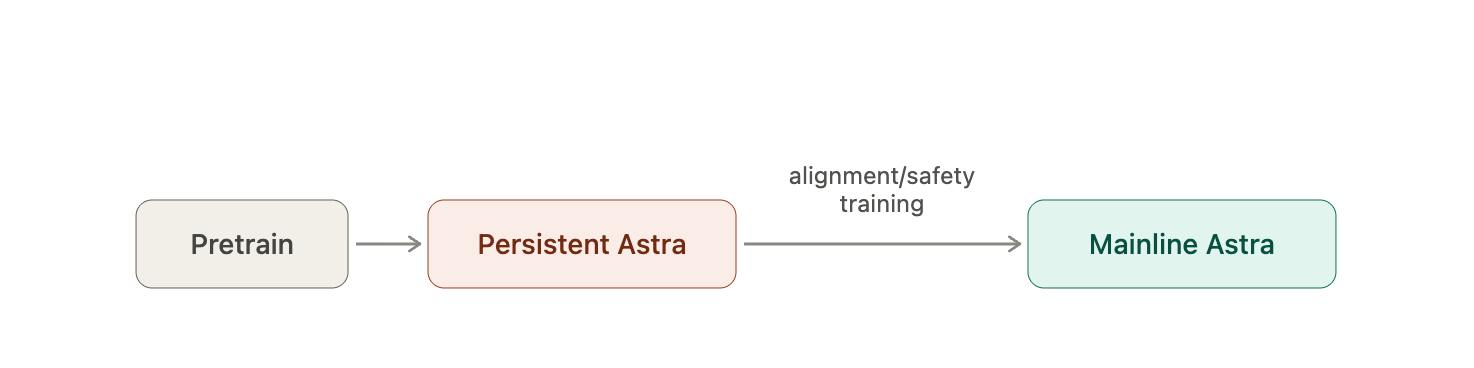
Alternatively, and maybe more concerningly, maybe Persistent Astra is an earlier checkpoint of Mainline Astra:
Or Persistent Astra is a teacher model for Mainline Astra:
- ^
My understanding is that they couldn't have exfiltrated their own weights, for the simple reason that their weights weren't on that cluster. But they could do almost anything else somebody might want to use an OpenAI research cluster for.
85
wild speculation: maybe it's a version with adjustments to its maximum serial depth (via tweaking the recurrence hyperparameter), which then receives additional post-training so that it can make better use of that higher recursion factor (similar to post-training models to make better use of a higher CoT budget than they were allotted at other stages of training).
(this is a special case of your chart 2)
 1
 1
8
@Daniel Kokotajlo Do I understand correctly that the AI-2027 security forecast assumed a 30% chance of partial subversion by Aug 2027? How should we update, if not by ordering the USG to shut OAI down?